spotted a possible bug in latest WP Cerber Version(s?) 9.8.3.
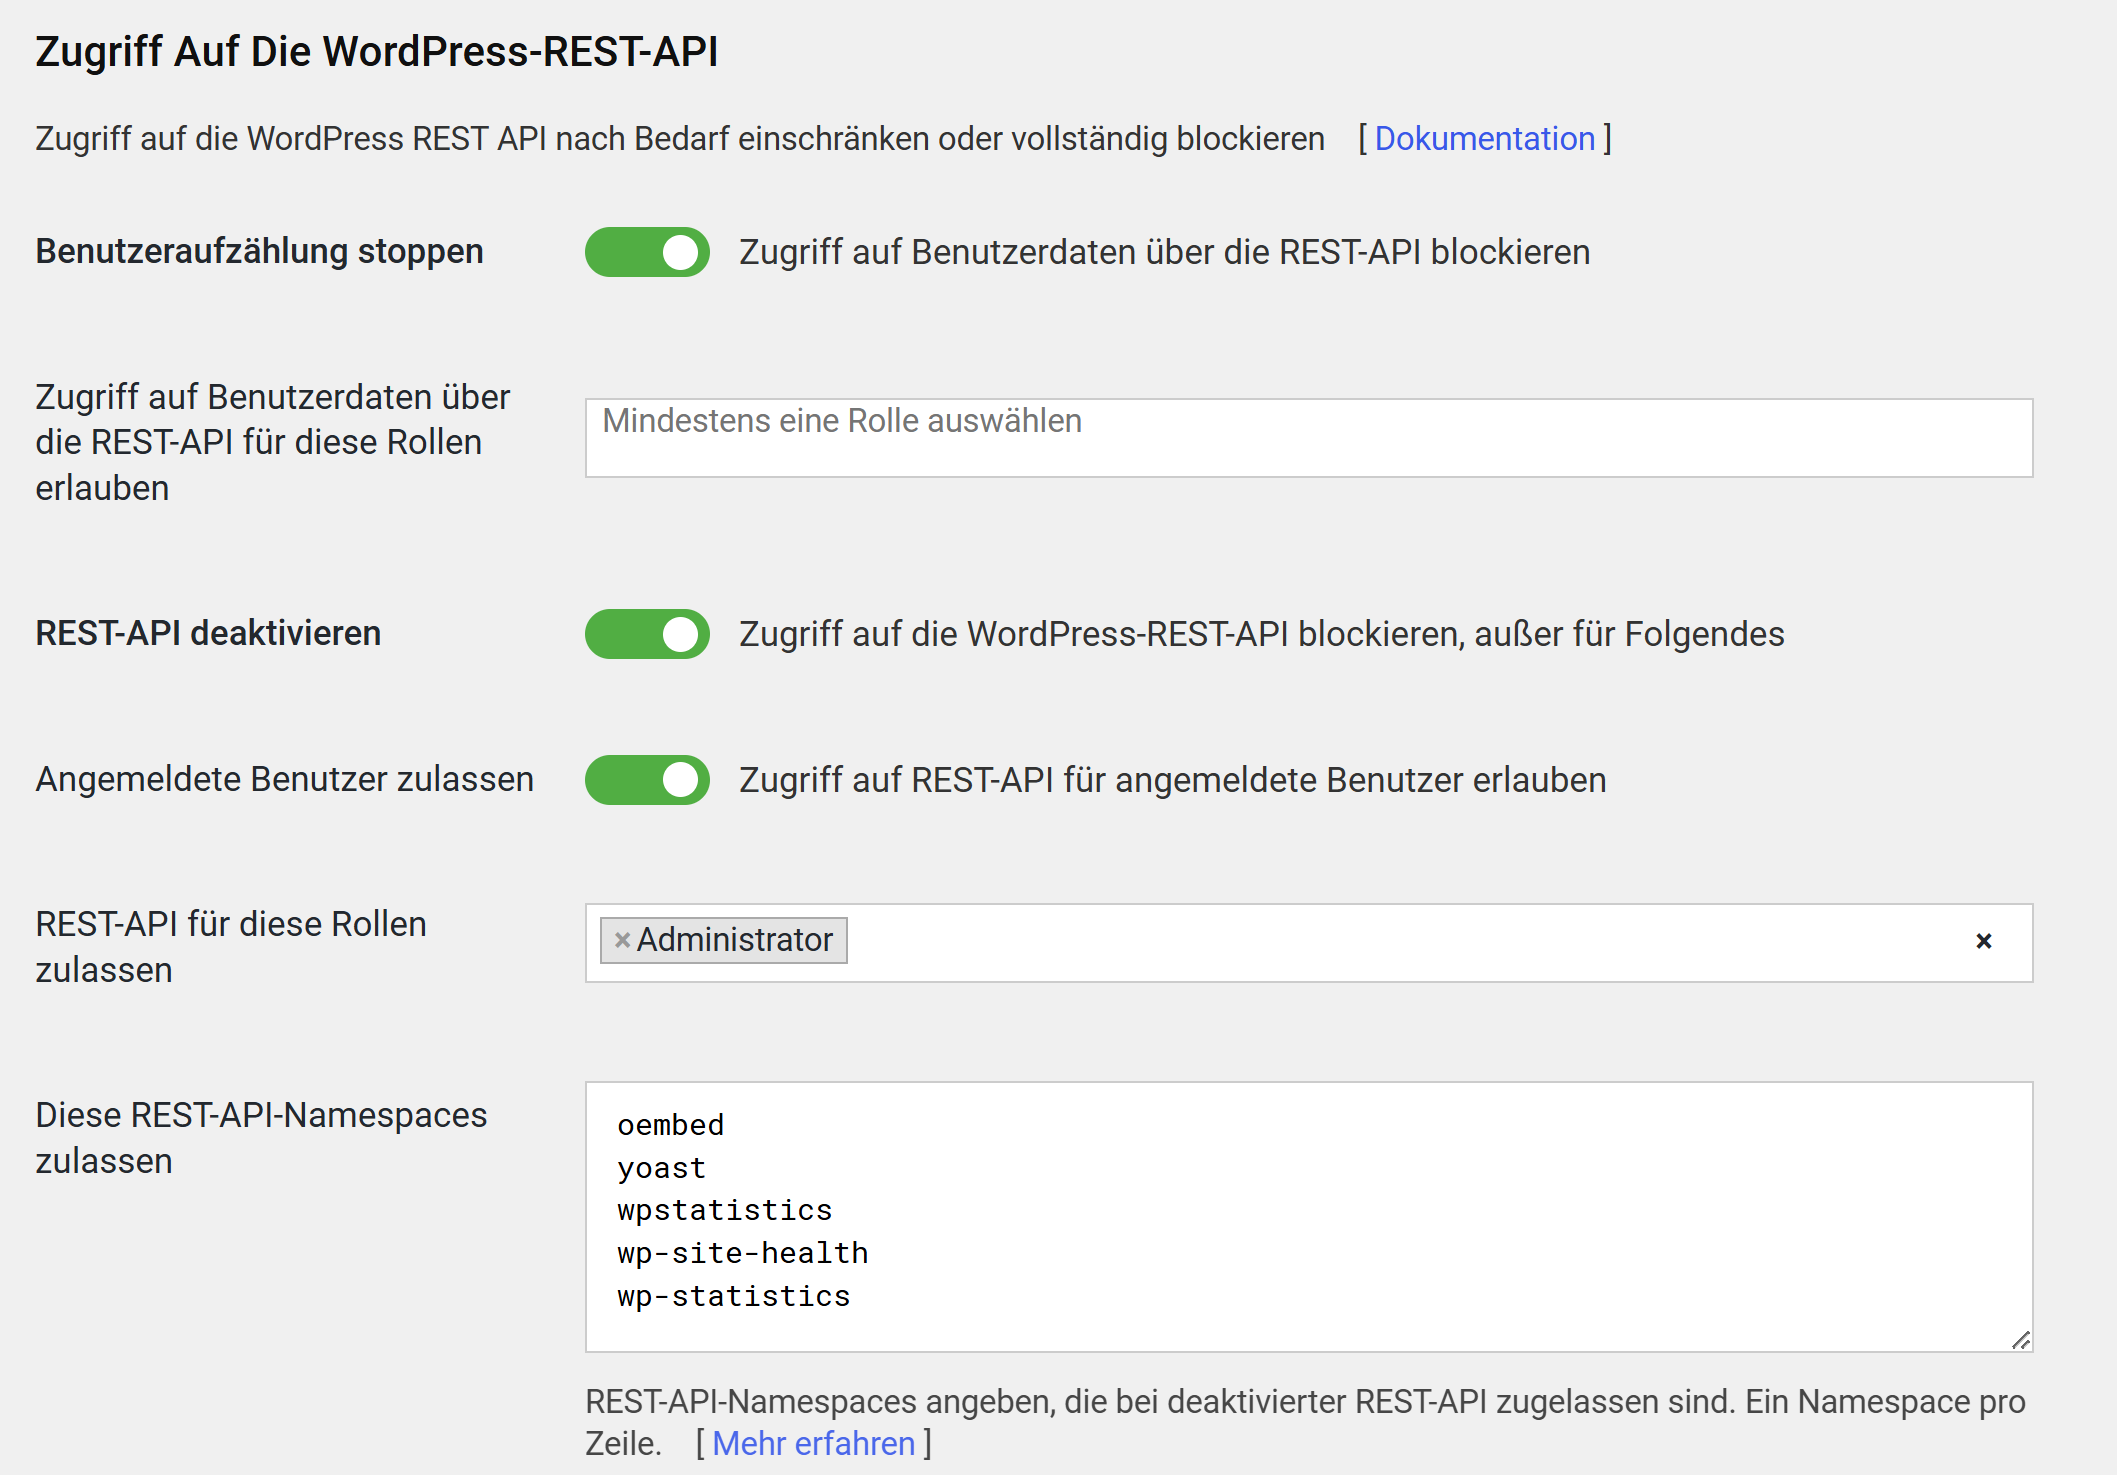
Even if in hardening section “deactivate REST-API” switch is activated it is possible to access /wp-json and read website details that should be hidden.
Tested with multiple wp-sites and clients.
Would be fantastic if this could be fixed and access to wp-json would be forbidden.
Worth to mention:
Access to admin user is enabled by default.
Test was done with several other devices and browsers that had no active logged on user/admin to check the unauthenticated user experience/their permissions.
It seems you are asking about the /wp-json/ REST API root endpoint.
One important point is that access to /wp-json/ does not necessarily mean that REST API protection is not working. This URL returns the WordPress REST API index. Depending on the WP Cerber configuration and the installed plugins, WordPress may allow access to the REST API root while restricting access to individual REST API endpoints.
Do you want WP Cerber to block access to the WordPress REST API for unauthenticated visitors entirely, including the /wp-json/ root endpoint?