Hi, I have an entry under “Top Offending IP Addresses” showing “127.0.0.1 localhost.localdomain.” It is probing the usual URLs like “/settings_production.py” and “/wp-config.php.backup” then gets locked out. I realize that spoofing is going on but can WP Cerber detect this? Is 127.0.0.1 really locked out? Or is the IP of this bad actor locked out? How can I see the IP of the actor behind this spoofing? Thanks in advance and great product BTW.
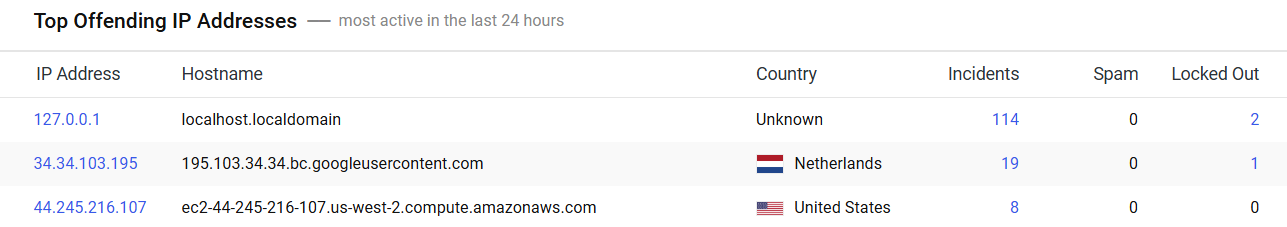
WP Cerber logged these requests as coming from 127.0.0.1 because that is the IP address your server environment passed to WordPress. The hostname localhost.localdomain is commonly associated with this local address, so this does not necessarily indicate IP spoofing.
Since WP Cerber could not see a separate external IP behind these requests, 127.0.0.1 itself was locked out.
This usually happens for one of two reasons:
-
Proxy configuration: Your hosting setup uses a local reverse proxy that is not passing the visitor’s original IP address to WordPress. Usually it’s passed in the
X-Forwarded-Forheader. -
Server-side activity: The requests were generated directly on the server. This could be a cron job, a security scanner, another local process, or malware running under this or another account on a shared server.
What you can do
Ask your hosting provider to find these requests in the web server and reverse proxy access logs. They can search for the requested URLs, such as /settings_production.py and /wp-config.php.backup, using the date and time shown in the WP Cerber log.
If those log entries show an external IP address, the proxy configuration should be checked because that IP address was not passed to WordPress.
If the web server logs also show 127.0.0.1, ask your hosting provider to check whether the requests passed through an intermediate proxy or load balancer. If no original IP was recorded there either, they will need to identify which local process or hosting account generated the requests.
If you keep seeing lockouts for 127.0.0.1, we recommend asking your hosting provider to investigate the server and proxy configuration, as well as other websites or hosting accounts on the same server, to rule out malware or unwanted server-side activity.
1 Like